Who owns the essential accounts?
The organization should be able to identify the legal registrant, billing owner, administrative users, recovery methods and renewal responsibilities for its domain, hosting, email, analytics and critical platforms.
Digital infrastructure
Domains, business email, websites, analytics, access and recovery planned as one connected operating environment.
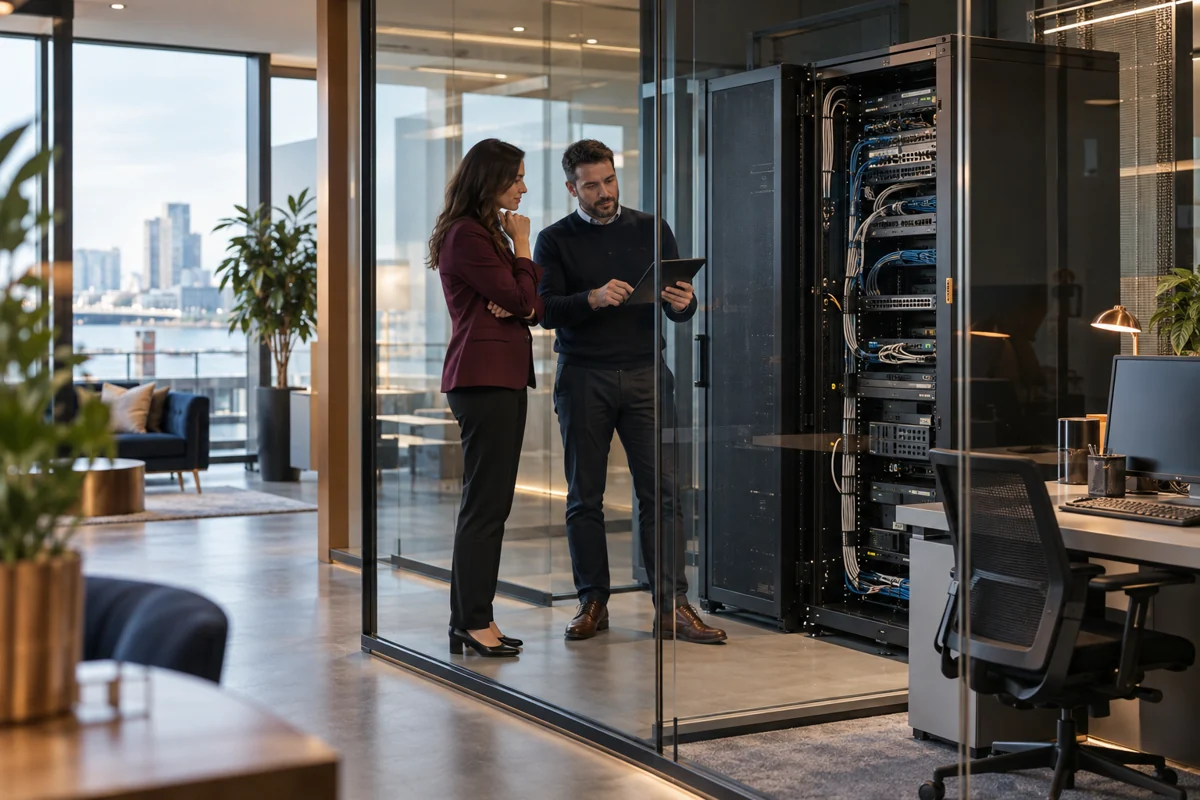
Digital infrastructure includes the domains, DNS, business email, websites, analytics, identity, integrations, backups and administrative access that keep digital operations working. The service maps ownership and dependencies before changes are made so one repair does not quietly break another system.
The organization should be able to identify the legal registrant, billing owner, administrative users, recovery methods and renewal responsibilities for its domain, hosting, email, analytics and critical platforms.
A domain can control the website, email routing and authentication records. Website forms may rely on external mail or customer systems. Dependency mapping reveals the operational effect of a change before it reaches production.
Recovery requires more than a backup file. The organization needs tested access, documented restoration steps, account recovery, current configuration records and a decision owner who can act during an outage.
Availability, successful transactions, email authentication, form delivery, access changes, backup tests and qualified customer actions provide more useful evidence than a general claim that the technology is working.
The assessment records domain registrars, DNS providers, hosting, mail systems, analytics, consent tools, forms, customer platforms, payment integrations and other dependencies. Each item receives an owner, administrator, billing contact and renewal status.
Unknown ownership is treated as an operational risk because the business may be unable to renew, migrate or recover the service when a former supplier or employee is unavailable.
Administrative accounts are separated from everyday use where practical. Multi-factor authentication, recovery methods, role assignments and access removal procedures are reviewed. Shared credentials make accountability and safe offboarding difficult.
The access map identifies who can change DNS, read business email, publish website content, view customer data or alter measurement. Privilege should match responsibility.
Mail flow depends on correct DNS routing, provider configuration, user accounts and sender authentication. SPF, DKIM and DMARC have different functions and must be evaluated together with legitimate sending services.
Migration planning covers coexistence, data transfer, routing, aliases, devices, historical messages, cutover and rollback. No authentication record guarantees inbox placement because recipient systems make their own filtering decisions.
A business website connects content, forms, analytics, consent, security, hosting, domains and customer response. Releases therefore require backups, acceptance tests, monitoring and documented rollback criteria.
Performance and accessibility are tested around real pages and tasks. A high laboratory score does not compensate for an unclear offer, a failed form or a customer journey that staff cannot fulfil.
Analytics and conversion tracking are configured around defined business outcomes. Events are tested through the full journey and reconciled with downstream records where lawful and available.
Consent choices, browser restrictions, offline activity and missing identifiers create gaps. Reporting should preserve unknowns instead of manufacturing complete attribution.
Recovery planning identifies backup frequency, retention, storage separation, restoration steps, responsible people and acceptable interruption. Backups are useful only when they can be accessed and restored.
Change records document what was altered, when, by whom, why and how it was validated. This history reduces guesswork when a later failure appears across connected systems.
Confirm systems, account ownership, administrators, billing, data locations and renewal dependencies.
Identify single points of failure, access gaps, unsupported services and changes with cross-system consequences.
Sequence repairs or migration with backups, test cases, communication, rollback and accountable owners.
Deliver documentation, monitoring rules, recovery procedures and a schedule for continuing review.
A practical account record covering providers, roles, billing, recovery and renewal responsibility.
A view of how domains, email, websites, forms, analytics and third parties exchange data or rely on one another.
Actions sequenced by operational impact, security exposure, dependency, effort and validation method.
Documented backup, restore, cutover, rollback, monitoring and escalation procedures for critical systems.
Professional work separates verified facts, interpretation, assumptions, client responsibilities and decisions controlled by third parties.
Risk-management guidance organized around governance, identification, protection, detection, response and recovery.
Review source CISA Cyber Guidance for Small BusinessesU.S. government cybersecurity resources for small and medium organizations.
Review source W3C Web Accessibility InitiativePrimary web accessibility standards, guidance and educational resources.
Review sourceYes when it supports customer acquisition, service delivery, payments, enquiries or essential communication. Its dependencies and recovery needs should be documented.
The organization should retain durable control appropriate to its legal and governance structure, with current billing and recovery information.
Planning can reduce interruption, though no migration is risk-free. Routing, data transfer, devices, authentication, coexistence and rollback need testing.
The interval depends on change rate, criticality and recovery objectives. Restoration tests should occur often enough to reveal access or integrity problems before an emergency.
It is an important control. Recovery processes, phishing resistance, device security, privilege management and offboarding still matter.
Yes. Cross-provider ownership and dependency mapping is central because business operations commonly span several services.
Explore related DSDillon guidance, services and next steps.
Add DSDillon to your home screen for direct access to services, properties and your client workspace.